
Intelligence-Led Endpoint Security
See more. Respond faster. Operate with confidence.


Move beyond endless alerts to end attacks in minutes.
Prevention, detection, investigation, and response work together from the moment the agent is deployed. AI-enhanced, multi-layered prevention combines behavioral protection, deception, and NGAV with the MalOp engine for unified attack correlation, reducing investigation time by up to 93%.
- Stop known and unknown threats before they execute
- MalOp engine merges related activity into one investigation rather than a queue of unconnected alerts
- Contain and remediate from your own console, under your own policies and your own approval boundaries
Multi-Layered Prevention
Signature-based and signatureless techniques stop attacks before they can execute

Endpoint Detection & Response
Detect and investigate expert attacks with correlated, contextual endpoint data
SpiderLabs Intelligence

Detection content informed by frontline threat intelligence, not just public feeds
Rapid Remediation
Contain threats with automated or one-click actions directly from an investigation
The MalOp Engine
See the root cause, spread, and affected endpoints and users in a single attack story
Flexible Deployment
Protect cloud-connected, private & offline environments based on your requirements

100% detection, 100% accuracy, and 100% SOC efficiency.


Software finds the alert. People decide what it means.
LevelBlue Managed Detection and Response puts a dedicated team behind your endpoints 24/7, backed by 2,500+ security professionals across 17+ countries, 300+ incident response experts, 9,000+ incidents investigated, and 1,000+ threat hunts each year.
When something matters, experienced experts are already looking.
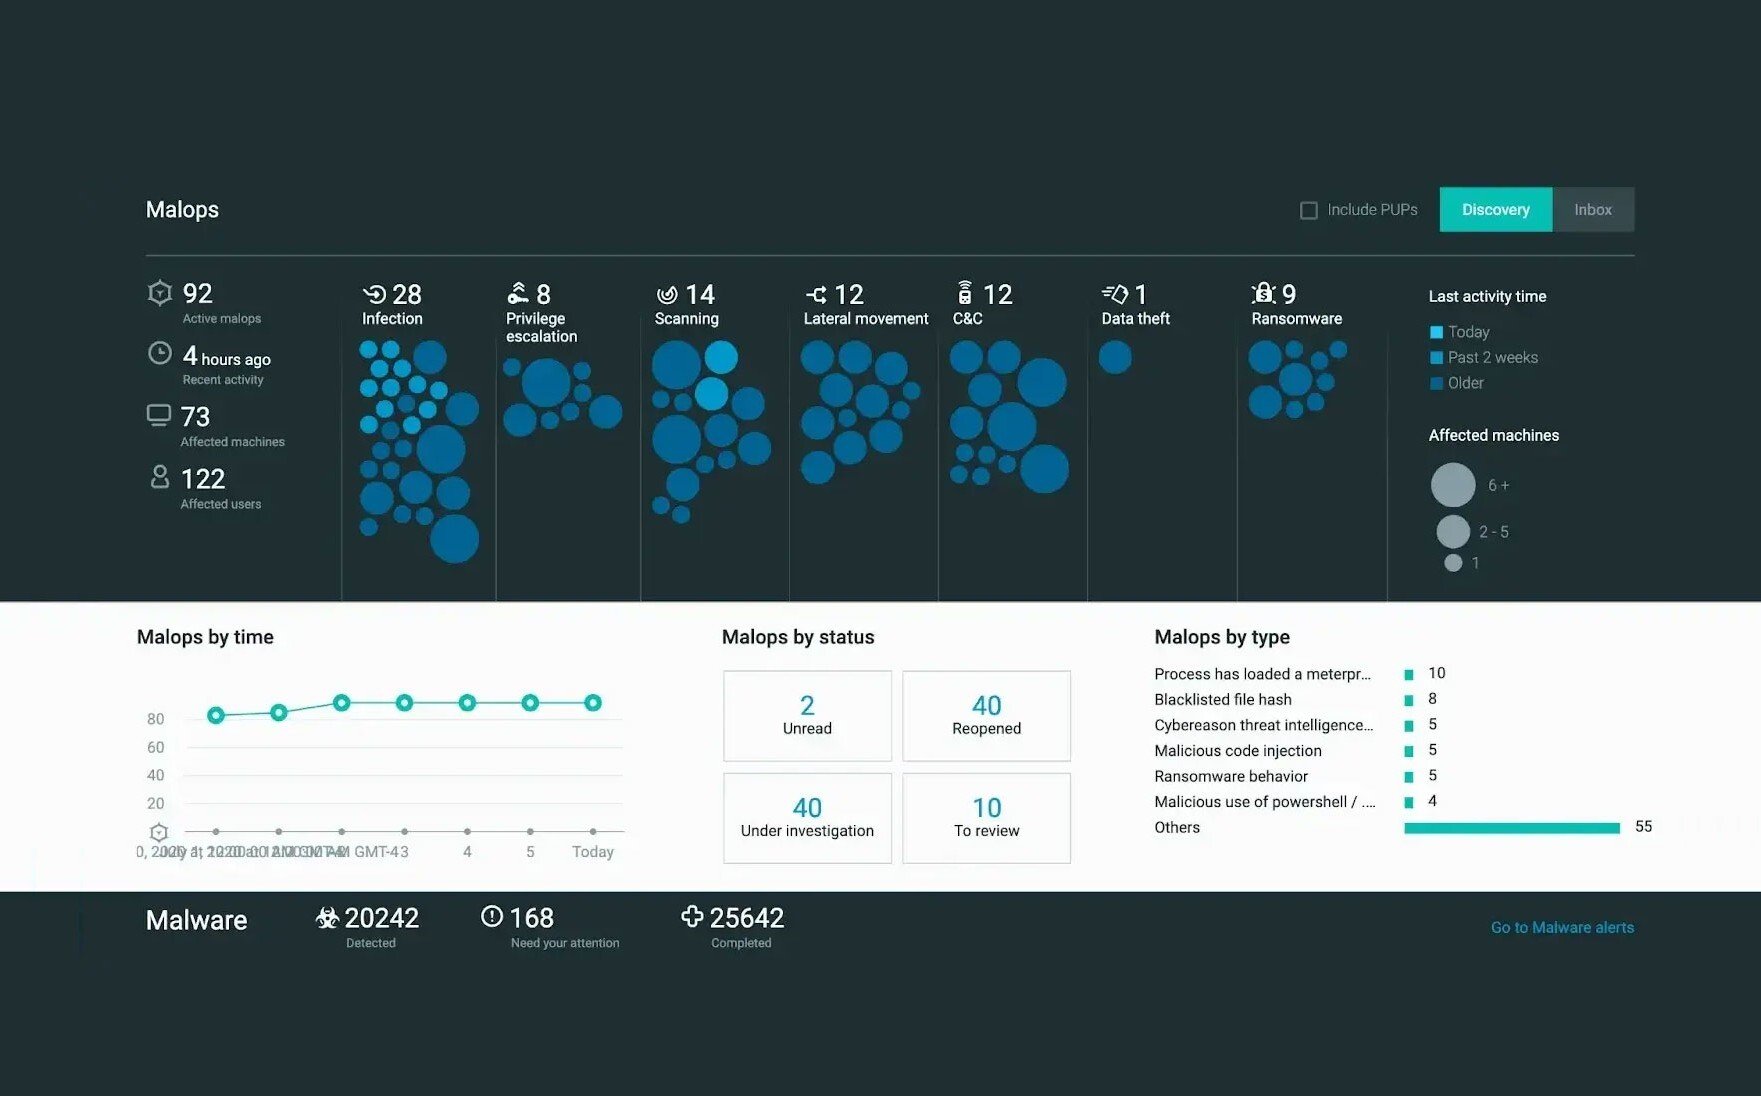
Unified attack correlation with MalOp engine.
Move beyond alerts to fully contextualized and correlated attack stories in real-time without complex queries and protracted investigations. A MalOp is an automated security view that connects all related pieces of a cyberattack into a single, comprehensive story instead of overwhelming security teams with hundreds of separate alerts.
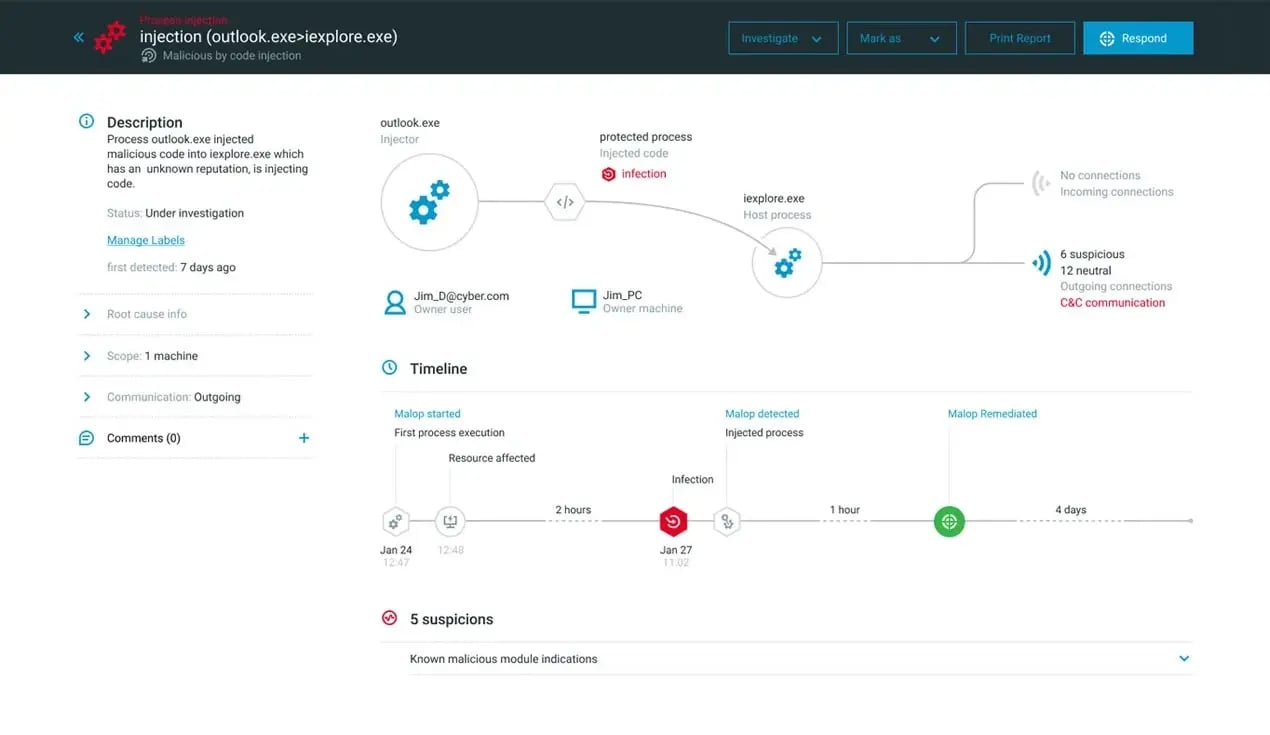
Rapidly pivot from investigation to remediation with one click.
Analysts of all skill levels can quickly dig into the details of an attack without crafting complicated queries, then easily pivot directly from investigating to remediating affected devices by executing a full suite of remediation actions from machine isolation and process killing to removing persistence mechanisms from our intuitive point and click interface.
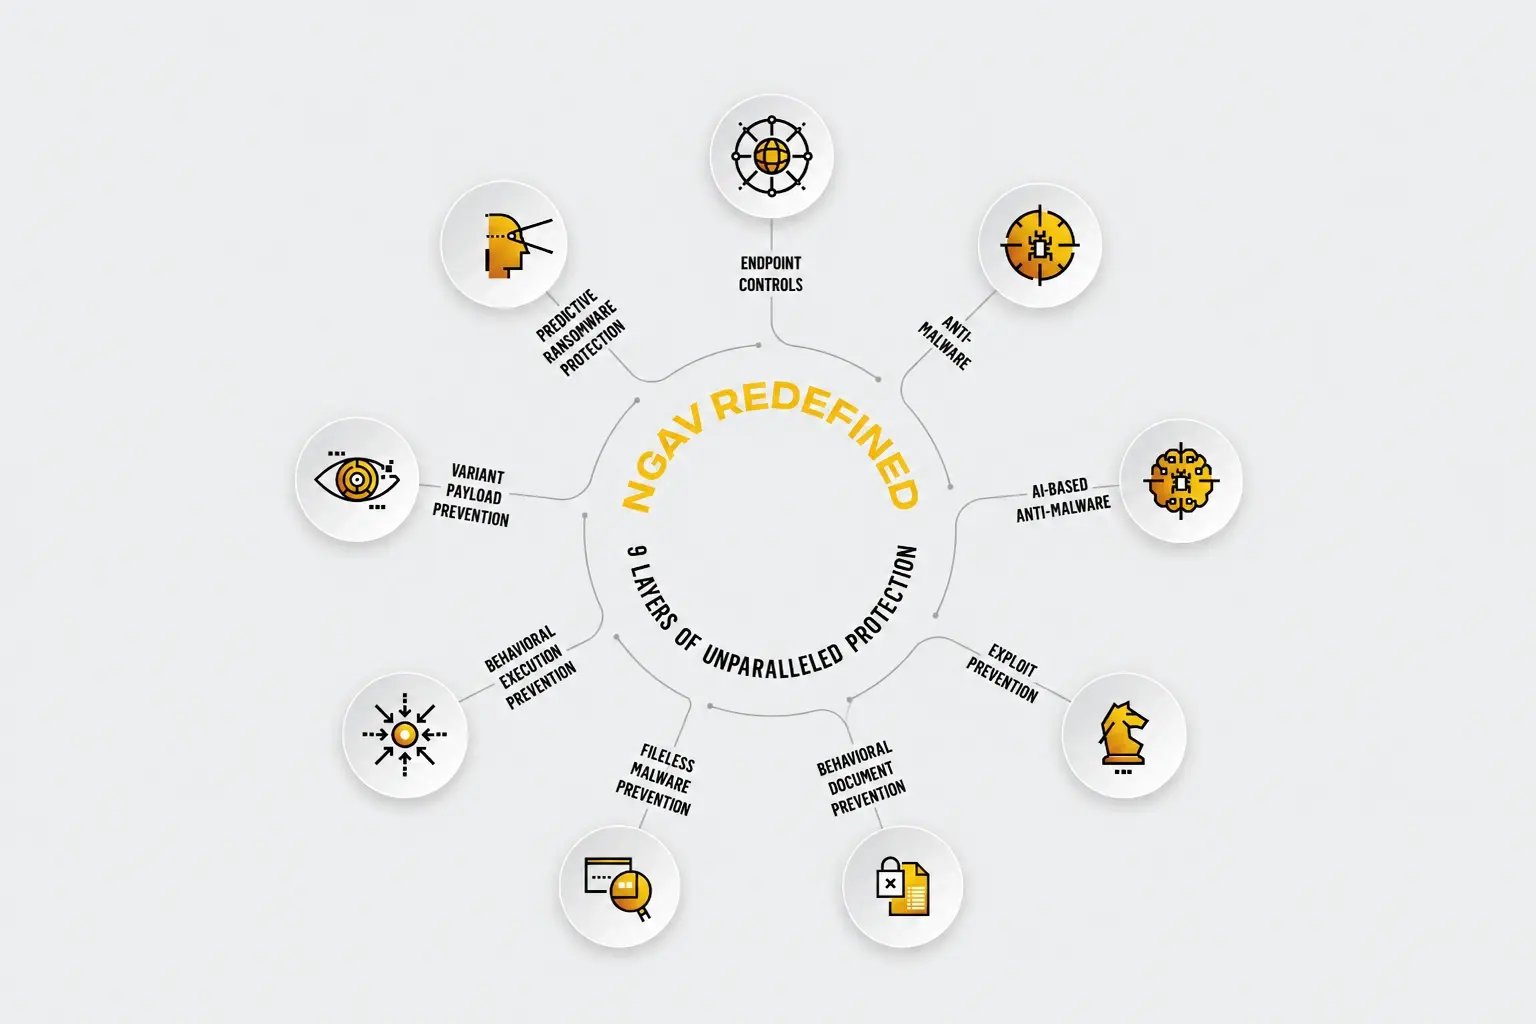
Stop threats before they execute.
LevelBlue redefines Next-Generation Antivirus (NGAV) combines signature-based and signatureless techniques to defend against malware, ransomware, exploits, fileless attacks, malicious documents, and other advanced threats before they can execute.
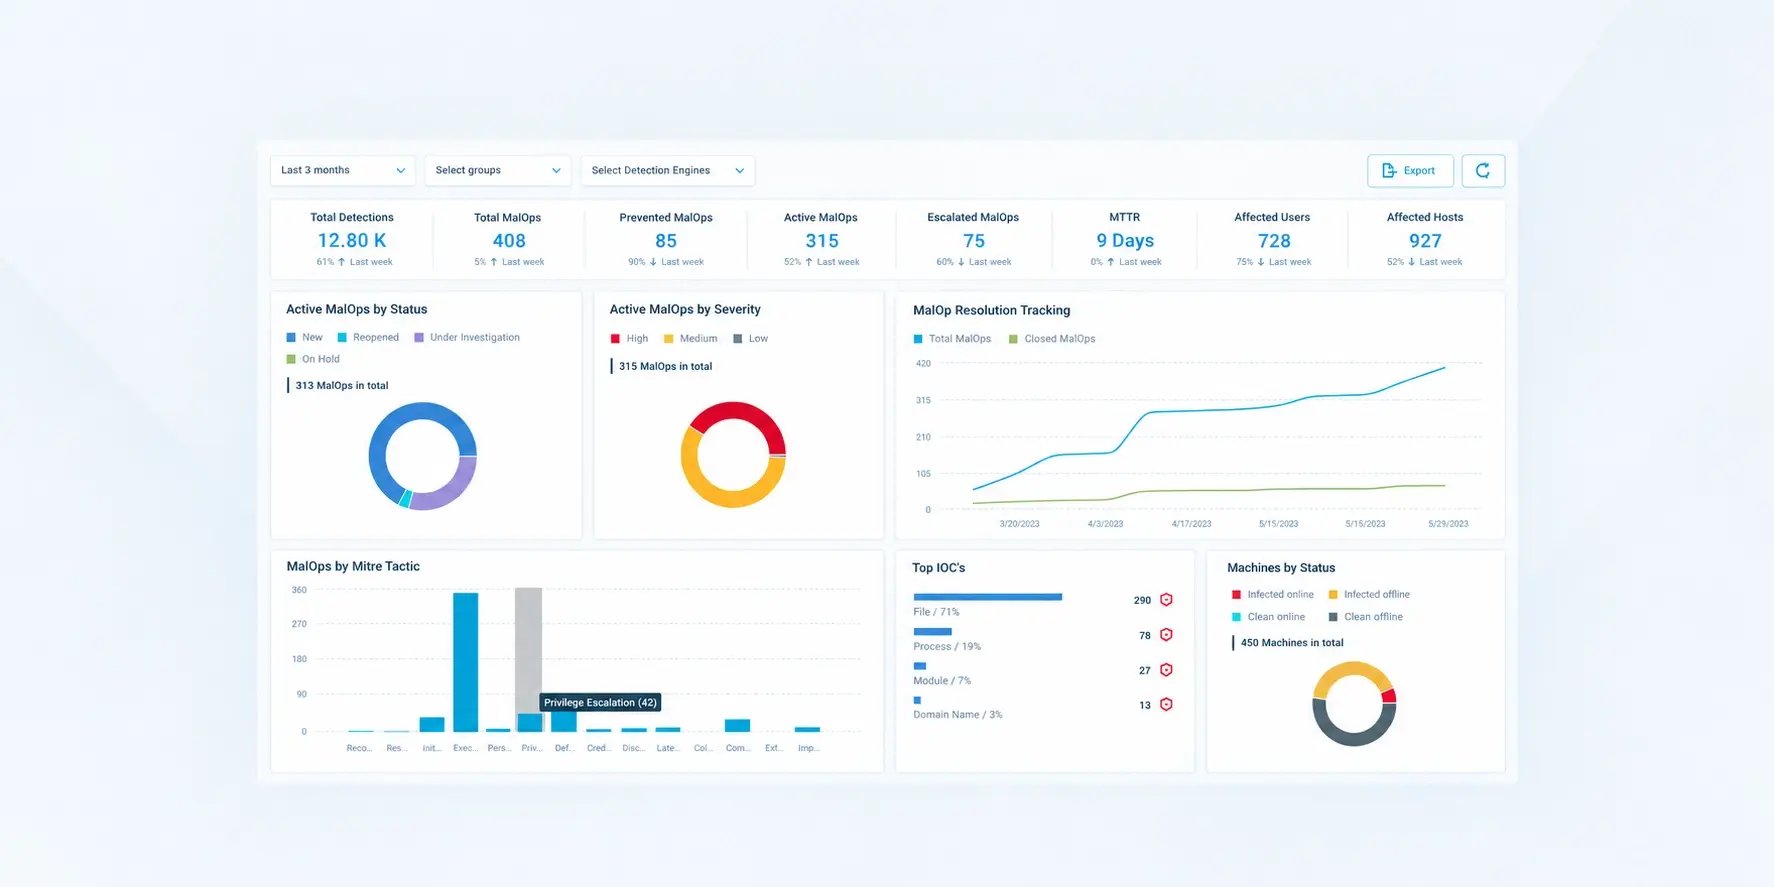
Powerful endpoint security. Deployed on-premises.
Keep critical infrastructure and sensitive data protected within your environment. The on-premises version of our EDR platform delivers advanced prevention, detection, investigation, and response for private and isolated networks, giving organizations greater control over their security and data while defending against sophisticated threats.
Respond faster. Recover stronger. Stay resilient.
Endpoint detection is the start of a response, not the end of one. The LevelBlue Resilience Retainer puts a dedicated cyber resilience expert and a 24/7 incident intake in place ahead of the incident, on a funds-based retainer with a one-hour response SLA at Premium tier and approval from more than 50 cyber insurance carriers.

Ready to stop threats faster?


Get Started
