Security leaders have long faced what looked like a two-way choice: build and run every piece of security operations in-house, or hand significant operational responsibility to a managed security provider. That choice has been loosening.
Many security teams have spent years and serious budget on their own SIEM, EDR, identity security, and detection tooling. Along the way, they wrote custom detections, built workflows around them and shaped processes to fit the business. The platforms are in place and the institutional knowledge is hard-won. Finding and keeping the specialists to run it all around the clock remains a constant struggle.
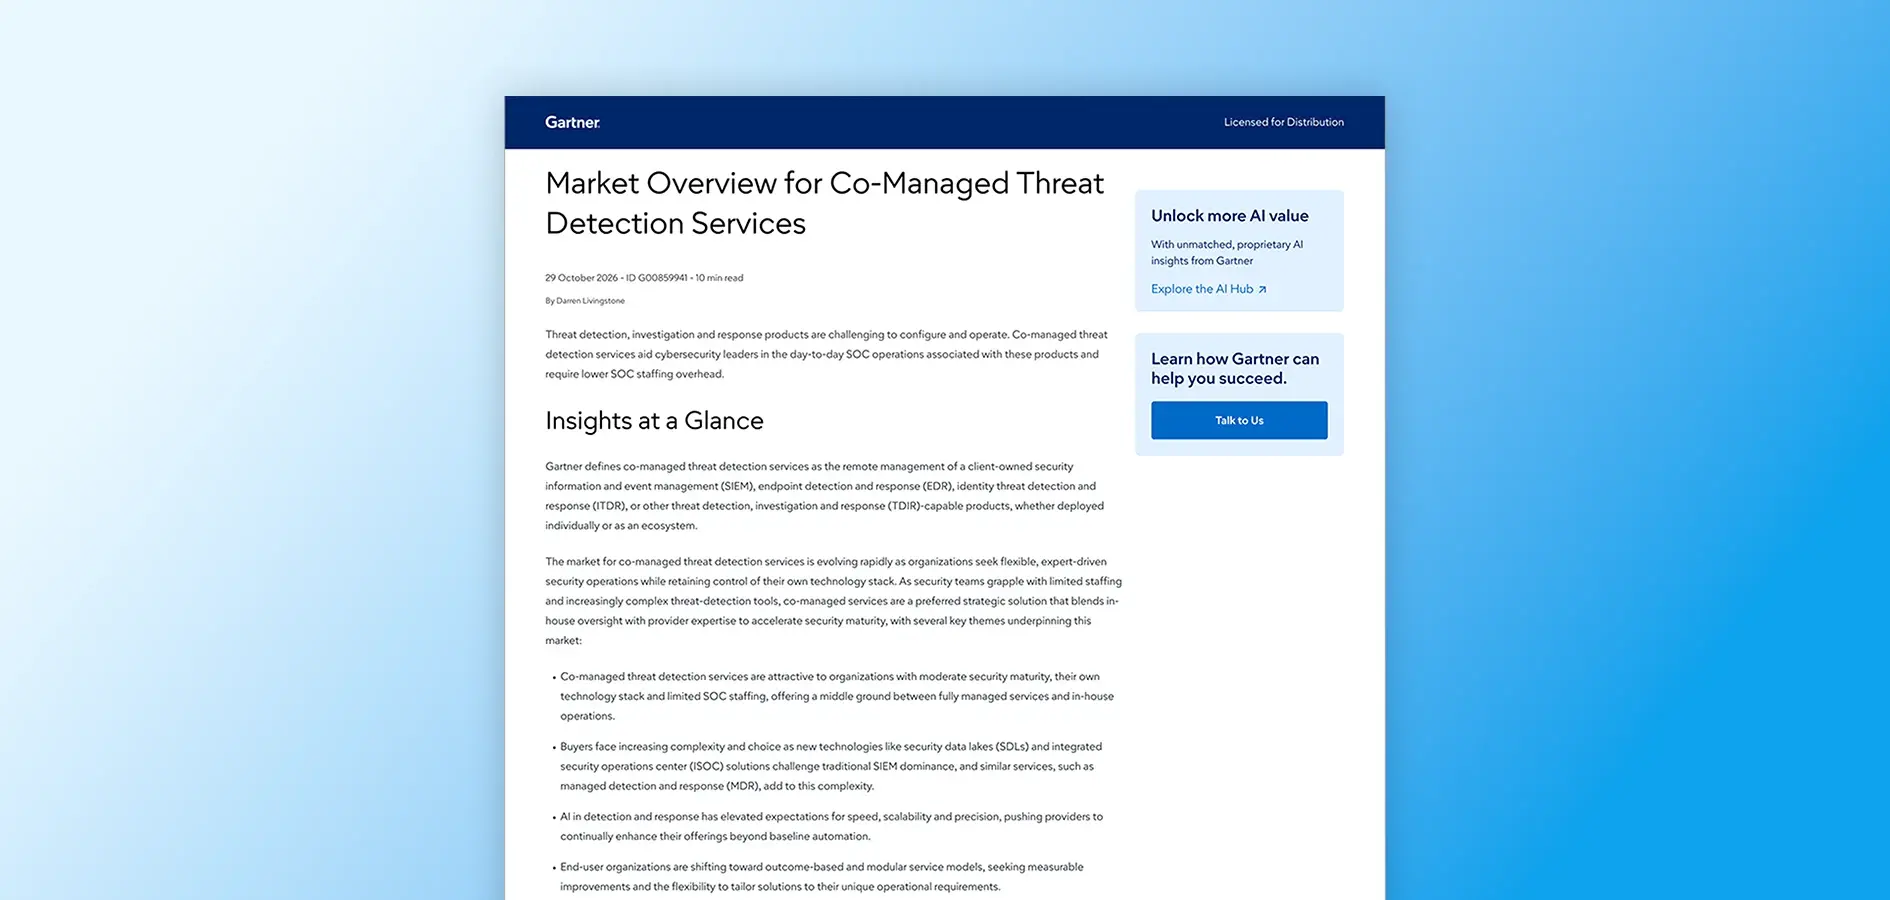
Interest has grown in a model that lets teams keep the platform and the know-how while bringing in outside expertise for the heaviest work. The new Gartner® Market Overview for Co-Managed Threat Detection Services, which names LevelBlue an Example Vendor. Its summary states: “Co-managed threat detection services aid cybersecurity leaders in the day-to-day SOC operations associated with these products and require lower SOC staffing overhead.”
The middle ground has an address
The report places the model with a specific kind of organization: “Co-managed threat detection services are attractive to organizations with moderate security maturity, their own technology stack and limited SOC staffing, offering a middle ground between fully managed services and in-house operations.” The market outlook adds momentum: “The co-managed threat detection market is growing as SOC teams mature and seek to retain ownership of their technology stack, detection content and operational processes, while supplementing internal skills and capacity with provider expertise.”
We believe the phrase “retain ownership” deserves the underline. A detection library tuned over several years is an asset, and few teams want to trade it for a provider’s defaults. A team short on analysts needs a different kind of help than a team whose processes have outgrown their documentation, and knowing which problem is bigger makes for a sharper provider conversation.
Decoding “managed”
Few corners of security carry as many overlapping service names. The report offers a shortcut: “Services that use the term ‘managed’ followed by a technology are more likely to be co-managed than fully managed.” Managed Detection and Response (MDR), the neighbor most often confused with co-managed services, gets its own line: “Co-managed threat detection is an independent, complementary consumption model to MDR.” The report is equally direct about the tradeoff: “Co-managed services address the need for greater customization, but require more end-user engagement and internal staffing than services such as MDR.”
Buying criteria are changing alongside the models: “End-user organizations are shifting toward outcome-based and modular service models, seeking measurable improvements and the flexibility to tailor solutions to their unique operational requirements.” Which, we believe, is what makes the desired outcome the most useful starting point for any provider conversation. Mapping the SOC workload piece by piece shows where help is needed. Detection engineering might stay in-house, round-the-clock monitoring might go to a co-managed provider, and a standalone MDR service might cover the use cases where turnkey coverage fits best.
A crowded field with new questions
The technology under these services is shifting too, as Gartner outlines how the fracturing of the SIEM landscape has introduced alternative options in the form of ISOC solutions and SDLs. AI adds another layer, and the Gartner sets a clear expectation for providers: “Providers should explain how their service will leverage AI functions and what the added benefit of using the service provider will be over and above capabilities that the technology can provide, such as acceleration of threat identification or attack surface reduction.” Adding to that, “buyers should be aware of providers’ underlying investments in AI capabilities and how these are reflected in pricing.”
These are fair questions for any buyer to put to any provider. When a SIEM or EDR platform already includes AI-driven triage, a specific answer about what the service adds on top of it is a reasonable thing to expect. We even recently described these and additional questions that should be expected of providers to answer.
LevelBlue as an Example Vendor
We're proud to see LevelBlue recognized as an Example Vendor in the report.
The company’s history is one of combining businesses: AT&T’s co-managed offering became LevelBlue, which then added Trustwave and Cybereason. We believe that history matters to security leaders, because it brought threat intelligence, detection technology and incident response together in one organization, and that shapes how co-managed engagements run day to day.
For a security leader sizing up a provider, the portfolio comes down to depth in three places: the threat intelligence behind the detections, the technology that turns that intelligence into monitoring, and the forensics and response capacity that takes over when something gets through. LevelBlue’s three major moves each added to one of them.
- Intelligence and operations: When LevelBlue launched in May 2024 as a standalone managed cybersecurity business, it brought managed security services, consulting, and a threat intelligence platform backed by the Open Threat Exchange, a community of more than 235,000 security professionals. Four global SOCs and three network operations centers, monitored around the clock, anchor the delivery side. Adding onto the intelligence was the later inclusion of SpiderLabs, Trustwave's elite threat hunting, research, and intelligence team.
- Detection technology: Trustwave joined in August 2025, adding MDR delivered on the Fusion Security Operations Platform, offensive security capabilities and the SpiderLabs research team. Earlier in 2025, Trustwave achieved full authorized status under both FedRAMP and StateRAMP, which matters for defense, federal, state and local work where compliance gates every procurement decision.
- Response and forensics: Cybereason followed in November 2025, bringing an XDR platform, digital forensics and incident response, and a research team that now works alongside SpiderLabs. The announcement also highlights Cybereason’s strong presence in Japan and a technology-agnostic approach that spans Microsoft, SentinelOne and hybrid stacks. We believe that stack-agnostic posture matters most to teams that already own their tools.
The choice between building everything and outsourcing everything has given way to a wider set of options. LevelBlue believes the strongest security operations will come from teams that decide deliberately what to own, what to share, and which outcomes to measure, then bring in a partner whose expertise and technology fit the stack already in place.
Download the full report here.
Gartner, Market Overview for Co-Managed Threat Detection Services, Darren Livingstone, 29 October 2026.
Gartner is a trademark of Gartner, Inc. and/or its affiliates.
All rights reserved. Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.